Vulnerabilities
Researchers Disclose Nine-Year-Old "RefluXFS" Linux Flaw Giving Local Users Root on Default RHEL Installs
Another long-standing Linux root escape lands — defender verification for RHEL-based environments this week.
Vulnerabilities
Another long-standing Linux root escape lands — defender verification for RHEL-based environments this week.
Artificial Intelligence (AI)
Google joins the vendor-side AI-cybersecurity race with Gemini 3.5 Flash Cyber and managed CodeMender - federal-adjacent defender partnerships this week.
Policy & Government
CISA's new directive ends CVSS-led patching for federal agencies — risk becomes the prioritization signal, and the most dangerous bugs must be patched in three days.
Vulnerabilities
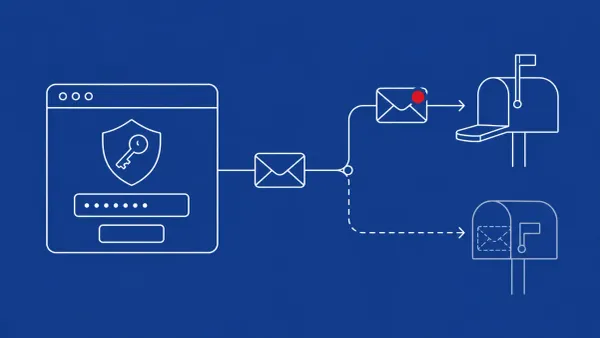
A critical flaw in the Kirki WordPress plugin (CVE-2026-8206, CVSS 9.8) lets an unauthenticated attacker send any account's password-reset link — including an admin's — to their own email and seize it. Versions 6.0.0–6.0.6 are fixed in 6.0.7; BleepingComputer reports exploitation.
Vulnerabilities
CISA added CVE-2024-21182 — an unauthenticated Oracle WebLogic flaw patched in July 2024 — to its Known Exploited Vulnerabilities catalog on evidence of active exploitation. Despite 'RCE' framing elsewhere, CISA describes unauthorized access to WebLogic data; agencies must patch by June 4.
Artificial Intelligence (AI)
Google Cloud launched AI Threat Defense on May 27, 2026 — an automated platform that pairs Gemini, the Wiz cloud-security stack, and the CodeMender AI code-fixing agent to find, prioritize, and patch software vulnerabilities at machine speed.
Policy & Government
India's CERT-In issued guidelines on May 26, 2026 requiring organizations to patch critical internet-exposed vulnerabilities within 12 hours, "where feasible." The cited reason is explicit: AI-driven exploitation has compressed the patch window past what conventional SLAs can survive.
Vulnerabilities
Microsoft patched CVE-2026-45659, a CVSS 8.8 deserialization RCE in SharePoint Server. The 'authenticated' precondition is barely a precondition — any account with Site Member, the lowest SharePoint role, can trigger it. Patch this week.
Artificial Intelligence (AI)
Anthropic says Project Glasswing's Claude Mythos Preview has surfaced more than 10,000 high- or critical-severity vulnerabilities in roughly a month. The numbers move the defender bottleneck: finding flaws is no longer the hard part — verifying, disclosing, and patching them is.
Supply Chain Attack
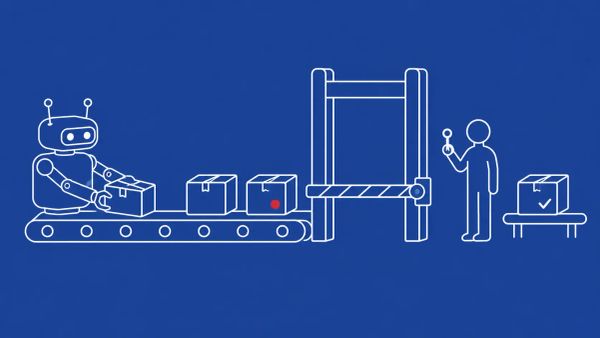
GitHub has made npm staged publishing generally available. A direct publish no longer ships a package; the tarball waits in a stage queue until a maintainer passes a 2FA challenge to approve it. It is the first ecosystem-level structural answer to the 2026 supply-chain wave.
Cybersecurity 101
Vulnerability management is the continuous cycle of finding, prioritizing, fixing, and verifying security weaknesses. This guide covers the lifecycle, risk-based prioritization with CVSS, EPSS and CISA KEV, and the shift toward CTEM.
Vulnerabilities
Trend Micro's own Incident Response team discovered CVE-2026-34926, a directory-traversal zero-day in Apex One, while it was being exploited. CISA added it to the KEV catalog with a June 4 federal deadline. Its modest 6.7 CVSS score conceals an environment-wide blast radius.