
Phishing
Microsoft and Trend Micro Document Blockchain-Abuse Phishing Against EU and Asia Hospitality
Two vendor-documented hospitality-sector phishing campaigns land the same week — sector-advisory work for hotel-industry defenders this week.
Phishing
Two vendor-documented hospitality-sector phishing campaigns land the same week — sector-advisory work for hotel-industry defenders this week.

Nation-State Cyber Threats
A Russian-intelligence campaign against messaging-app credentials, documented by Ukraine, uses fake support texts to coax Signal and WhatsApp users into surrendering the codes that unlock their accounts.
Phishing
Days before the June 11 kickoff, the FBI and researchers warn that FIFA World Cup 2026 fraud is already live — thousands of lookalike FIFA domains, banking malware hidden in pirate streaming apps, and login pages cloned well enough to take over real accounts.

Phishing
Kali365, the phishing-as-a-service kit the FBI flagged in May for stealing Microsoft 365 tokens past MFA, has broadened its targets to AWS, Okta, Xerox DocuShare and Russian services, Arctic Wolf reports — extending its core OAuth device-code phishing to far more of the stack.

Social Engineering
A phishing wave is impersonating Signal Support to ask users for their secret recovery key — the key that decrypts online backups containing past messages. The defender utility is simple: Signal will never ask for it, ever.

Phishing
The FBI's IC3 has warned organizations about Kali365, a Telegram-sold phishing-as-a-service kit that runs device-code phishing against Microsoft 365 — stealing the OAuth tokens issued after the victim genuinely passes MFA on Microsoft's real sign-in page.
Phishing
The Australian Signals Directorate's Australian Cyber Security Centre published an advisory on May 7, 2026 warning that pro-criminal threat actors are using compromised legitimate Australian WordPress websites as launch pads for ClickFix social-engineering attacks delivering the Vidar Stealer information-stealing malware. Visitors to compromised Australian business
Phishing
Securonix tracked a phishing campaign that has compromised more than 80 organizations — mostly U.S.-based — by abusing legitimate SimpleHelp and ConnectWise ScreenConnect remote-monitoring tools. The lure impersonates the U.S. Social Security Administration. The architecture is dual-RMM redundancy: when defenders detect one channel, the other persists. Securonix

Phishing
Microsoft Defender Research disclosed a sophisticated AiTM phishing campaign that hit 35,000+ users at 13,000+ organizations across 26 countries in just three days. 92% of targets were in the U.S. The lure was a fake employee disciplinary case. The reverse proxy stole session tokens — bypassing MFA in
Threat Intelligence
CTM360 names FEMITBOT — a shared backend running crypto scams, fake AI tools, and Android malware impersonating Apple, NVIDIA, Disney, and the BBC, all inside Telegram.
Threat Intelligence
The OAuth phishing kit is plumbed end-to-end through legitimate SaaS, which is exactly the point.
Trending
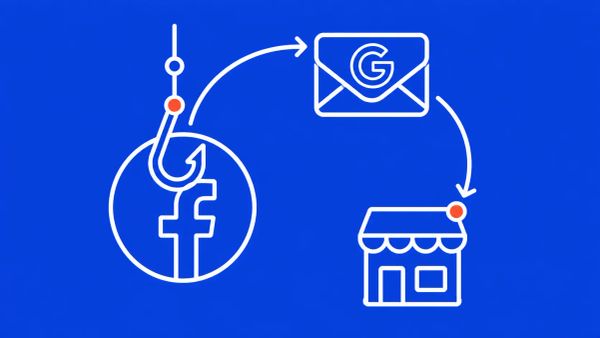
Vietnamese-linked operation "AccountDumpling" has compromised 30,000 Facebook Business accounts by sending phishing emails from Google's legitimate AppSheet address — bypassing spam filters and running a criminal resale storefront for stolen accounts.