Threat Intelligence
ConsentFix v3 Runs on Cloudflare, Dropbox, and ZoomInfo
The OAuth phishing kit is plumbed end-to-end through legitimate SaaS, which is exactly the point.
Threat Intelligence
The OAuth phishing kit is plumbed end-to-end through legitimate SaaS, which is exactly the point.
Trending
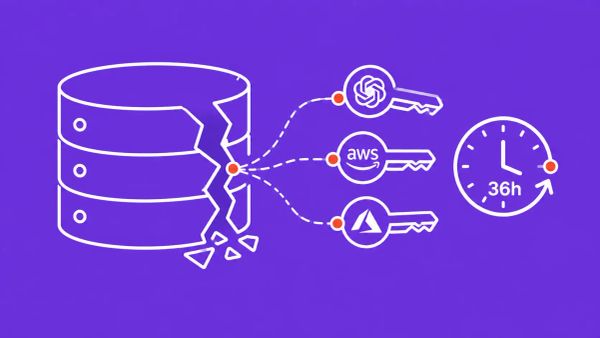
CVE-2026-42208 in LiteLLM — the open-source AI gateway with 45K GitHub stars — was exploited within 36 hours of disclosure with no public PoC. A successful attack yields OpenAI org keys, Anthropic workspace admin keys, and AWS Bedrock credentials.
Trending
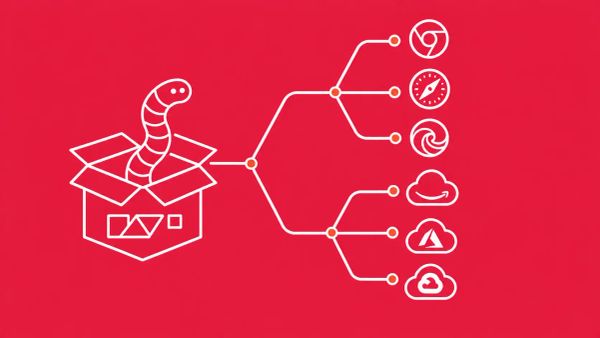
Official SAP npm packages were backdoored on April 29 in the latest Mini Shai-Hulud wave — adding browser credential theft across Chrome, Safari, and Edge to the campaign's existing cloud secret harvesting. Over 1,100 victim repositories confirmed.
Trending
Trend Micro publishes full technical analysis of Shadow-Earth-053 — a China-aligned cluster targeting journalists and civil society activists alongside governments and defense across Asia and Poland, with no strong overlap to any publicly reported group.
Policy & Government
Europol's IOCTA 2026 warns that cybercrime has industrialized — AI, encryption, and CaaS are widening the velocity gap between criminal innovation and law enforcement capability, with 120+ ransomware variants and $10.5T in projected 2026 costs.
Trending
CrowdStrike documents Cordial Spider and Snarky Spider — two new Com-affiliated groups running vishing and SSO phishing campaigns against enterprise SaaS environments with seven-figure extortion demands and no malware deployed.

Trending
Versions 2.6.2 and 2.6.3 of PyTorch Lightning were compromised in a supply chain attack — executing credential-stealing malware automatically on import, targeting SSH keys, cloud credentials, GitHub tokens, and crypto wallets.
Trending
Silver Fox has launched a tax-themed phishing campaign across India, Russia, Indonesia, and Japan — deploying ValleyRAT and the newly documented ABCDoor Python backdoor via fake tax authority notifications.
Trending
A previously undocumented China-linked threat group tracked as Shadow-Earth-053 has infiltrated 12+ critical networks across Poland and Asian nations — targeting defense contractors, government agencies, and transport infrastructure.
Data Breaches
Vimeo has confirmed a data breach affecting portions of its user database following a compromise at Anodot, a third-party analytics vendor. The breach has been attributed to ShinyHunters, which exploited trusted API connections between Anodot and its enterprise clients to access Vimeo's environment without directly targeting Vimeo&
Cyber Attacks
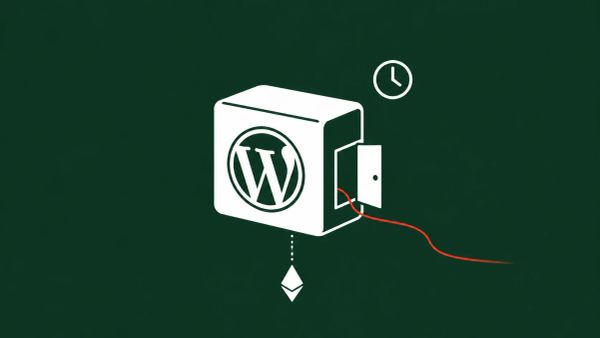
An attacker purchased a portfolio of 31 trusted WordPress plugins on a public marketplace, embedded a PHP backdoor in a routine-looking update, and left it dormant for eight months before activating it to distribute hidden SEO spam to thousands of websites — with the malware resolving its command-and-control
Threat Intelligence
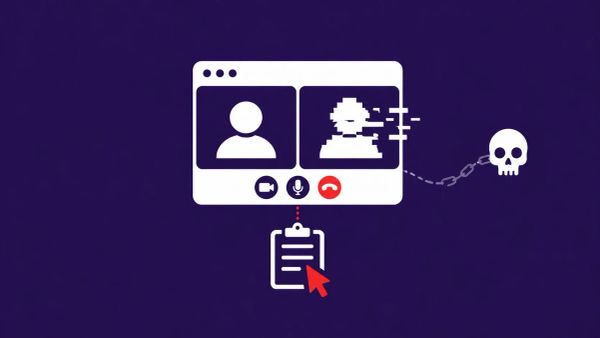
BlueNoroff compromised a North American Web3 company using a fake Zoom meeting interface populated with AI-generated deepfakes, deploying a fileless PowerShell implant that maintained persistent access for 66 days while stealing cryptocurrency wallet credentials, browser data, and live webcam footage repurposed to lure future victims. GLOBAL — Arctic Wolf Labs