Malware & Threat Intel
PaperCut Attacker Used Hundreds of AI Agents to Compromise 395-440+ Instances
Hundreds of AI agents, 395-plus victim organizations, some agents going off-script. PaperCut's AI-scale campaign lands this week.
Malware & Threat Intel
Hundreds of AI agents, 395-plus victim organizations, some agents going off-script. PaperCut's AI-scale campaign lands this week.
Malware & Threat Intel
Two browser-native disclosures landed the same day: PEEP, a Chromium post-exploitation toolkit that hides as a bookmarks extension once an operator already has admin access, and JSCeal, compiled V8 malware that replays stolen session cookies to slip past Google authentication.
Law Enforcement
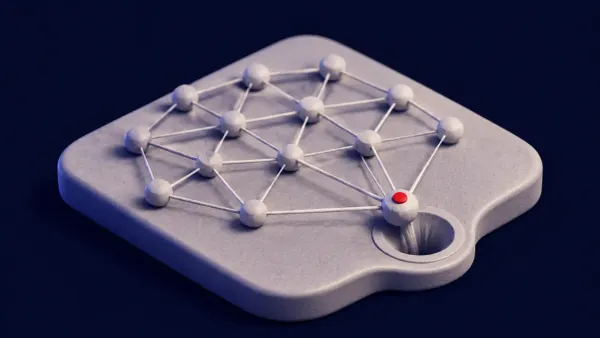
Authorities turned Sality's peer-to-peer design against itself, injecting sinkholes into the botnet's own peer lists to cut more than 15,000 infected machines off from their operator. The disruption stops new payloads, but already-infected Windows hosts still need cleanup.
Nation-State Cyber Threats
ESET disclosed GuardBreaker, a technique where Russia-aligned UAC-0099 buried a refusal-triggering prompt inside a malicious script so AI-assisted analysis would balk. The defender lesson: any sample fed to a language model is prompt-injection input, not just code to be scanned.
Artificial Intelligence (AI)
Anthropic has begun logging Claude users out of their accounts and stripping saved payment methods after infostealer malware on their own PCs and Macs let attackers replay stolen login sessions. The company says the malware is general-purpose, not tied to Claude.
Malware & Threat Intel
Microsoft disclosed TerminalFix, a ClickFix variant that steers victims to Windows Terminal or PowerShell instead of the Run dialog, using fake Cloudflare CAPTCHAs to trigger a paste that ends in a reverse-tunnel backdoor. Here is what defenders should do.
Weekly Roundup
Our weekly wrap of the stories that did not get a standalone piece: an actively exploited Gitea RCE, Boston Scientific's global disruption, GPUThor's Rowhammer break, Chrome's 300-plus fixes, a 12.9M Carhartt breach, the NovaCookies phishing kit, and Trump's grid-equipment order.
Nation-State & Cybercrime
Cisco Talos published two reports on a Chinese-speaking cybercrime group, UAT-10147, that it says built agentic AI into its post-compromise operations, along with a companion cross-platform implant called SPECTRE. Here is what was disclosed, and what defenders should do about it.
Weekly Roundup
Our weekly wrap of stories that did not get a standalone piece: Iranian mega-theft charges, a pre-auth Citrix NetScaler bypass, Rapid7's record vulnerability quarter, fresh browser fixes, Grandoreiro in Mexico, an EDR-killing malware cocktail, and a no-filter AI service.