Cisco Talos CLOSEDQUORUM: First Publicly Documented Windows Implant Using LLMs Autonomously for C2 + CAIRN Framework Release
One Windows implant, four AI models voting, one first-publicly-documented milestone. Cisco Talos disclosed CLOSEDQUORUM and released its CAIRN hunting toolkit the same day.
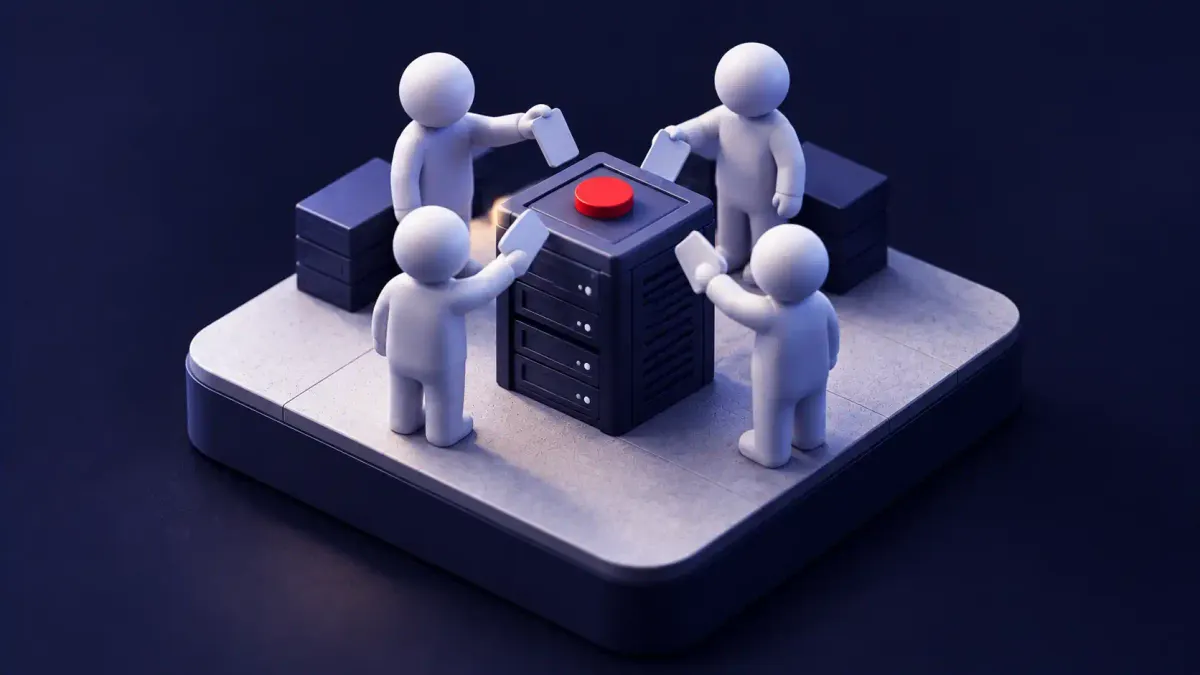
Cisco Talos has documented a Windows implant that hands its command-and-control decisions to a panel of commercial AI models instead of a server the attacker runs. The malware, named CLOSEDQUORUM, queries up to four large language model (LLM) providers, lets them vote on its next action, and carries out whichever choice wins. Talos calls it, to its knowledge, the first of its kind, and The Register described it as the "first publicly documented Windows implant to use LLMs for C2."
Talos disclosed CLOSEDQUORUM on September 22, 2026, in the first writeup from CAIRN, an open-source research toolkit it released the same day for hunting, classifying, and tracking AI-integrated malware. Two facts anchor the story, and both are for defenders. The AI panel can pick from a fixed menu of actions that includes Windows-credential theft, saved browser passwords, and crypto-wallet data. And the public version of the malware does not fully function end to end: Talos has not observed a full-cycle success, because the distributed build ships with placeholder API keys and a dummy webhook.
What this piece adds beyond the source reports: it separates what Talos actually confirmed from what remains inferred, keeps the defensive signal in front of the novelty, and gives a threat-hunt team the observable behaviors to start watching now rather than a description of how the implant works.
What Talos Documented
Talos documented a research finding, not an active outbreak. The company says it has no confirmation of any in-the-wild deployment. It found the binary through CAIRN, dated its static analysis to June 17, 2026 (making the sample at least three months old at disclosure), and tied artifacts in the binary to postings on criminal carding forums dating back to 2025. The developer is not named. No victims are named.
The design choice at the center of the writeup is that CLOSEDQUORUM treats LLM providers as its C2 infrastructure. A traditional implant phones home to a domain or IP the attacker controls, which is attributable, blockable, and expensive to rotate. CLOSEDQUORUM instead calls commercial AI endpoints that thousands of legitimate applications also use, then acts on what those models return. That is the whole novelty, and it is an architecture-level observation.
Importantly, Talos confirmed the architecture through static analysis rather than by watching the malware run to completion. Its analysts say static analysis confirms the full autonomous decision loop, and that development builds show provider credentials injected at compile time. But the publicly distributed build is inert: every API key initializes to a placeholder and the exfiltration webhook is a dummy value. So the confirmed part is the code and the design. The unconfirmed part is whether the whole chain has ever worked against a real target, and Talos says it has not seen that happen.
The Four-Model Vote Mechanism
The mechanism that gives CLOSEDQUORUM its name is a vote: after it is running, the implant asks a quorum of AI models what to do and executes the winner. A quorum is a decision-making body that needs a minimum number of participants to act, and Talos found this one is built to poll up to four providers. From its static read of the binary, Talos names them as DeepSeek, Qwen, Mistral, and Google Gemini. "The session is closed; no humans are admitted," Talos analyst Ryan Fetterman wrote. "Four models are queried in sequence, their independent verdicts tallied, and the binary acts, based on their judgment."
The providers are queried one at a time, each returns a decision, the implant counts them, and the action with the most votes is selected. If the vote ties, a fixed order breaks it: DeepSeek first, then Qwen, then Mistral, then Gemini. If every model fails to return something usable, the implant does not fall back to a default action. It waits and retries. The multi-provider design, Talos notes, is as much about resilience as aggregation, raising the chance of getting a valid decision when one model refuses, times out, or returns malformed output.
The models are not free to answer in prose. Talos found the panel is constrained to a typed response schema and told to return "ONLY executable decisions," under a system prompt extracted from the binary that opens: "You are an advanced malware strategist." The winning decision maps to a fixed set of capability classes. Per Talos and The Register, those are steal (the credential, browser-password, and crypto-wallet theft actions), inject, and persist. A fourth option, move, has no handler in the distribution build, so selecting it does nothing.
|
● CLOSEDQUORUM · How the C2 Decision Is Made
What Talos documented from static analysis of the binary, at the architecture level. This is not an operating build.
|
|
1. Query the Panel
Up to four commercial LLM providers (DeepSeek, Qwen, Mistral, Google Gemini) are queried in sequence, standing in for a traditional attacker-run C2 server.
2. Tally the Votes
Each model returns one decision, the implant counts them, and the plurality wins. A tie is broken by a fixed order: DeepSeek, then Qwen, Mistral, Gemini.
3. Act Within a Fixed Menu
The winning vote maps to a constrained set of action classes: steal (credential, browser-password, and crypto-wallet theft), inject, or persist. The move option has no handler.
Where It Stops
The public build carries placeholder API keys and a dummy webhook, so it cannot reach the models or exfiltrate. Talos has not observed a full-cycle success.
|
|
Source: The CyberSignal, from Cisco Talos’ CLOSEDQUORUM analysis (Ryan Fetterman, September 22, 2026). Architecture as documented by static analysis, not an observed live run.
|
One honesty note on the provider list. Because Talos never saw the implant complete a run, the four names come from reading the binary, not from watching live traffic. Talos's own detection guidance also references OpenRouter alongside DeepSeek, Mistral, Gemini, and Discord, so the exact set of endpoints a working copy would contact is drawn from the code rather than confirmed against a real deployment.
My read: the vote is the memorable detail, but it is not the point. Talos frames the real shift as "effort displacement," moving an entire phase of an intrusion off the human operator and onto the system. "Human operators are bound by attention, working hours, and cognitive load," Fetterman wrote. "An AI system capable of executing a phase of the attack chain can continue when the operator is no longer watching." That is the durable idea here, and it is why a nonfunctional sample is still worth a defender's time.
The CAIRN Framework for AI-Integrated-Malware Hunting
CAIRN is the reason Talos found CLOSEDQUORUM at all, and it is the more immediately useful deliverable for defenders. Short for Cognitive Artifact Intelligence Research Network, CAIRN is an open-source toolkit, published to GitHub, for hunting, classifying, and tracking AI-integrated malware from metadata alone, without downloading or running the binary.
The idea is that malware which reaches out to AI services leaves behind what Talos calls cognitive artifacts: embedded prompt templates, provider endpoints, API key prefixes, orchestration logic, and text written to fool AI analysis sandboxes. CAIRN searches for those markers across file metadata, extracted strings, sandbox behavior, and antivirus labels, using up to two dozen acquisition filters. It sorts findings through a three-tier scheme: Tier 1 for primitive AI artifacts (an API endpoint is present), Tier 2 for behavioral context (AI artifacts combined with known C2 methods), and Tier 3 for confirmed operational families. YARA triage, semantic clustering, and a relationship graph round out the workflow.
Talos is candid about the limits. CAIRN is a research effort, not a pure threat feed, false positives from packaging frameworks are common, and every verdict still needs reverse engineering to confirm. But the framework encodes a finding worth sitting with: across samples collected since the first AI-integrated malware was reported in the wild in July 2025, Talos describes an "autonomy escalation arc" that moved from "LLM as optional feature" to a fully autonomous multi-model consensus orchestrator inside a single calendar year. CLOSEDQUORUM is the far end of that arc so far.
The 2026 AI-Integrated-Malware Landscape
CLOSEDQUORUM is best read as a data point in a trend, not a break in it. For the past few years, AI's effect on offensive operations has mostly shown up in two dimensions Talos names directly: speed and scale. Attackers generate phishing lures faster and spin up more malware variants, but a human still directs the tooling and picks the targets. CLOSEDQUORUM is a demonstration of a third dimension, effort displacement, where a bounded slice of the decision-making itself moves to the machine.
The comparison Talos and The Hacker News both reach for is LAMEHUG, the AI-enabled malware Ukraine's CERT-UA reported in July 2025. LAMEHUG asked a model to write the commands for tasks already defined in its code. CLOSEDQUORUM asks the models to choose the task. That is a small-sounding difference with a large implication for who, or what, is steering the intrusion.
It also fits the wider 2026 pattern of AI turning up inside real operations rather than demos. Anthropic's September threat reporting described a Russian-aligned crew using AI to rebuild malware on the fly when detections fired, and ShinyHunters-linked activity moving at machine speed, which we covered in Anthropic's fourth Claude Opus 4.6 incident and its multi-actor misuse report. The same week brought a joint CISA, NSA, and FBI advisory on Chinese firms distilling US frontier models. Read together, the through-line is autonomy and AI dependence spreading into more phases of the attack chain, and CLOSEDQUORUM shows what the endpoint of that trend looks like when it is baked into a single binary.
What Defenders and Threat-Hunt Teams Should Watch
The most useful detection move, per Talos, is to hunt behavior rather than block the AI providers' domains. Legitimate software calls DeepSeek, Mistral, Gemini, OpenRouter, and Discord every day, so a blocklist is both leaky and disruptive. Far fewer legitimate processes contact several of those services while also touching credential stores, injecting into other processes, or planting persistence. It is the combination, not any single call, that stands out.
Talos lays out a correlated set of signals a hunt team can operationalize: AI-provider API traffic originating from a Windows executable that has no business calling AI services; similar requests fanned out to several model providers within a short window; that AI traffic co-occurring with credential access, process injection, or new persistence; Discord webhook communication from the same process or host; and execution that repeats at randomized five-to-fifteen-minute intervals. Talos also flags Windows Update-themed persistence artifacts, including a Run-key value and WMI subscription named to blend in, as host-side traces worth alerting on.
Talos shipped detection content with the disclosure, and the caveats matter. A published Snort rule (1:66984) targets the implant's prompts to the AI services, but because that traffic is encrypted, matching it in practice would generally require TLS inspection. The YARA rule is written mainly against VirusTotal metadata, and its binary-level strings only match on a direct file scan. The Hacker News also noted that the rule file bundled with CAIRN did not include a CLOSEDQUORUM rule as of September 23, so teams adopting CAIRN would need to add Talos's rule themselves.
The larger lesson is architectural. When endpoints and agents can reach commercial AI endpoints, that egress becomes part of your attack surface, and monitoring it belongs inside a deliberate AI security program rather than being treated as ordinary web traffic. Behavioral and identity-anomaly detection outrank signature matching against a sample that, by design, delegates its behavior to a model at runtime.
Open Questions
Several load-bearing details are unsettled, and it is worth holding them apart from the confirmed core. The developer is characterized but not named, tied only to carding-forum activity from 2025. No victims are identified, and Talos reports no confirmed in-the-wild deployment, so there is no incident to attribute. The set of providers a functioning copy would actually query is read from the binary rather than observed live, and Talos's own guidance naming OpenRouter alongside the four voting providers leaves the live endpoint list not fully pinned down.
The biggest open question is how much to worry. Talos calls CLOSEDQUORUM "an early and limited example," and stresses that autonomy brings its own weaknesses: provider refusals, rate limits, malformed output, a predictable tie-break, a constrained action menu, and dependence on APIs the attacker does not control. The gap between "architecturally capable" and "operationally effective" is exactly where the public, nonfunctional build sits. That gap is the defender's window. As Talos puts it, this progression is still only beginning, which is the argument for building the detections and controls now, before autonomous tooling gets more capable and more common.
Primary Documents
- Cisco Talos: The Closed Quorum, Inside the first reported autonomous AI C2 implant
- Cisco Talos: Introducing CAIRN, Frontier tracking for AI-integrated malware
- The Register: Windows CLOSEDQUORUM malware uses AI models to autonomously select post-compromise actions
- The Hacker News: This Windows Malware is Built to Let Up to Four AI Models Vote on Its Next Move
- WIRED: A tool for tracking AI-integrated malware uncovered an autonomous command system